Cybersécurité
725 views | +2 today
Your new post is loading...
Scooped by Yannick Giquel
September 18, 11:22 AM

Multiples vulnérabilités dans WordPress - CERT-FR

Multiples vulnérabilités dans WordPress - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à la confidentialité des données Contournement de la politique de sécurité Injection de code indirecte à distance (XSS) Systèmes affectés WordPress versions antérieures à 7.1.1 Résumé De multiples vulnérabilités ont été découvertes dans WordPress. Elles permettent à un attaquant de provoquer une atteinte à la confidentialité des données, une injection de code indirecte à distance (XSS) et un contournement de la politique de sécurité. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité WordPress wordpress-7-1-1 du 17 septembre 2026 https://wordpress.org/news/2026/09/wordpress-7-1-1-maintenance-and-security-release/
No comment yet.
Scooped by Yannick Giquel
September 18, 11:09 AM

Multiples vulnérabilités dans le noyau Linux de Red Hat - CERT-FR

Multiples vulnérabilités dans le noyau Linux de Red Hat - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Exécution de code arbitraire Élévation de privilèges Systèmes affectés Red Hat CodeReady Linux Builder for ARM 64 - Extended Update Support 10.0 aarch64 Red Hat CodeReady Linux Builder for ARM 64 - Extended Update Support 10.2 aarch64 Red Hat CodeReady Linux Builder for ARM 64 - Extended Update Support 9.8 aarch64 Red Hat CodeReady Linux Builder for ARM 64 10 aarch64 Red Hat CodeReady Linux Builder for ARM 64 8 aarch64 Red Hat CodeReady Linux Builder for ARM 64 9 aarch64 Red Hat CodeReady Linux Builder for IBM z Systems - Extended Update Support 10.2 s390x Red Hat CodeReady Linux Builder for IBM z Systems 10 s390x Red Hat CodeReady Linux Builder for IBM z Systems 9 s390x Red Hat CodeReady Linux Builder for Power, little endian - Extended Update Support 10.0 ppc64le Red Hat CodeReady Linux Builder for Power, little endian - Extended Update Support 10.2 ppc64le Red Hat CodeReady Linux Builder for Power, little endian - Extended Update Support 9.8 ppc64le Red Hat CodeReady Linux Builder for Power, little endian 10 ppc64le Red Hat CodeReady Linux Builder for Power, little endian 8 ppc64le Red Hat CodeReady Linux Builder for Power, little endian 9 ppc64le Red Hat CodeReady Linux Builder for x86_64 - Extended Update Support 10.0 x86_64 Red Hat CodeReady Linux Builder for x86_64 - Extended Update Support 10.2 x86_64 Red Hat CodeReady Linux Builder for x86_64 - Extended Update Support 9.8 x86_64 Red Hat CodeReady Linux Builder for x86_64 10 x86_64 Red Hat CodeReady Linux Builder for x86_64 8 x86_64 Red Hat CodeReady Linux Builder for x86_64 9 x86_64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 10.0 aarch64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 10.2 aarch64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 9.2 aarch64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 9.4 aarch64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 9.8 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 10.2 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 8.10 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 9.2 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 9.4 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 9.8 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Update Support 10.0 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Update Support 10.2 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Update Support 9.8 aarch64 Red Hat Enterprise Linux for ARM 64 10 aarch64 Red Hat Enterprise Linux for ARM 64 8 aarch64 Red Hat Enterprise Linux for ARM 64 9 aarch64 Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 10.0 s390x Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 10.2 s390x Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 9.2 s390x Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 9.4 s390x Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 9.8 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 10.2 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 8.10 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 9.2 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 9.4 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 9.8 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Update Support 10.0 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Update Support 10.2 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Update Support 9.8 s390x Red Hat Enterprise Linux for IBM z Systems 10 s390x Red Hat Enterprise Linux for IBM z Systems 8 s390x Red Hat Enterprise Linux for IBM z Systems 9 s390x Red Hat Enterprise Linux for Power, little endian - 4 years of support 10.0 ppc64le Red Hat Enterprise Linux for Power, little endian - 4 years of support 10.2 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 10.2 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 8.10 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 9.2 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 9.4 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 9.8 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Update Support 10.0 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Update Support 10.2 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Update Support 9.8 ppc64le Red Hat Enterprise Linux for Power, little endian 10 ppc64le Red Hat Enterprise Linux for Power, little endian 8 ppc64le Red Hat Enterprise Linux for Power, little endian 9 ppc64le Red Hat Enterprise Linux for Real Time 8 x86_64 Red Hat Enterprise Linux for Real Time for NFV 8 x86_64 Red Hat Enterprise Linux for x86_64 - 4 years of updates 10.0 x86_64 Red Hat Enterprise Linux for x86_64 - 4 years of updates 10.2 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 10.2 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 8.10 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 9.2 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 9.4 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 9.8 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle Long Life 8.6 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Update Support 10.0 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Update Support 10.2 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Update Support 9.8 x86_64 Red Hat Enterprise Linux for x86_64 - Update Services for SAP Solutions 9.2 x86_64 Red Hat Enterprise Linux for x86_64 - Update Services for SAP Solutions 9.4 x86_64 Red Hat Enterprise Linux for x86_64 - Update Services for SAP Solutions 9.8 x86_64 Red Hat Enterprise Linux for x86_64 10 x86_64 Red Hat Enterprise Linux for x86_64 8 x86_64 Red Hat Enterprise Linux for x86_64 9 x86_64 Red Hat Enterprise Linux Server - AUS 8.6 x86_64 Red Hat Enterprise Linux Server - AUS 9.2 x86_64 Red Hat Enterprise Linux Server - AUS 9.4 x86_64 Red Hat Enterprise Linux Server for Power LE - Update Services for SAP Solutions 9.2 ppc64le Red Hat Enterprise Linux Server for Power LE - Update Services for SAP Solutions 9.4 ppc64le Red Hat Enterprise Linux Server for Power LE - Update Services for SAP Solutions 9.8 ppc64le Résumé De multiples vulnérabilités ont été découvertes dans le noyau Linux de Red Hat. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire, une élévation de privilèges et un déni de service à distance. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Red Hat RHSA-2026:67114 du 14 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67114 Bulletin de sécurité Red Hat RHSA-2026:67277 du 14 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67277 Bulletin de sécurité Red Hat RHSA-2026:67468 du 15 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67468 Bulletin de sécurité Red Hat RHSA-2026:67469 du 15 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67469 Bulletin de sécurité Red Hat RHSA-2026:67470 du 15 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67470 Bulletin de sécurité Red Hat RHSA-2026:67471 du 15 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67471 Bulletin de sécurité Red Hat RHSA-2026:67723 du 16 septembre 2026 https://access.redhat.com/errata/RHSA-2026:67723 Bulletin de sécurité Red Hat RHSA-2026:68100 du 16 septembre 2026 https://access.redhat.com/errata/RHSA-2026:68100 Bulletin de sécurité Red Hat RHSA-2026:68131 du 16 septembre 2026 https://access.redhat.com/errata/RHSA-2026:68131 Bulletin de sécurité Red Hat RHSA-2026:68507 du 17 septembre 2026 https://access.redhat.com/errata/RHSA-2026:68507 Bulletin de sécurité Red Hat RHSA-2026:68532 du 17 septembre 2026 https://access.redhat.com/errata/RHSA-2026:68532 Référence CVE CVE-2024-53161 https://www.cve.org/CVERecord?id=CVE-2024-53161 Référence CVE CVE-2024-58007 https://www.cve.org/CVERecord?id=CVE-2024-58007 Référence CVE CVE-2025-40026 https://www.cve.org/CVERecord?id=CVE-2025-40026 Référence CVE CVE-2025-40149 https://www.cve.org/CVERecord?id=CVE-2025-40149 Référence CVE CVE-2025-68745 https://www.cve.org/CVERecord?id=CVE-2025-68745 Référence CVE CVE-2025-71127 https://www.cve.org/CVERecord?id=CVE-2025-71127 Référence CVE CVE-2026-23103 https://www.cve.org/CVERecord?id=CVE-2026-23103 Référence CVE CVE-2026-23172 https://www.cve.org/CVERecord?id=CVE-2026-23172 Référence CVE CVE-2026-23466 https://www.cve.org/CVERecord?id=CVE-2026-23466 Référence CVE CVE-2026-31479 https://www.cve.org/CVERecord?id=CVE-2026-31479 Référence CVE CVE-2026-31539 https://www.cve.org/CVERecord?id=CVE-2026-31539 Référence CVE CVE-2026-31566 https://www.cve.org/CVERecord?id=CVE-2026-31566 Référence CVE CVE-2026-31656 https://www.cve.org/CVERecord?id=CVE-2026-31656 Référence CVE CVE-2026-31663 https://www.cve.org/CVERecord?id=CVE-2026-31663 Référence CVE CVE-2026-43114 https://www.cve.org/CVERecord?id=CVE-2026-43114 Référence CVE CVE-2026-43133 https://www.cve.org/CVERecord?id=CVE-2026-43133 Référence CVE CVE-2026-43233 https://www.cve.org/CVERecord?id=CVE-2026-43233 Référence CVE CVE-2026-43248 https://www.cve.org/CVERecord?id=CVE-2026-43248 Référence CVE CVE-2026-43339 https://www.cve.org/CVERecord?id=CVE-2026-43339 Référence CVE CVE-2026-43368 https://www.cve.org/CVERecord?id=CVE-2026-43368 Référence CVE CVE-2026-43370 https://www.cve.org/CVERecord?id=CVE-2026-43370 Référence CVE CVE-2026-45998 https://www.cve.org/CVERecord?id=CVE-2026-45998 Référence CVE CVE-2026-46054 https://www.cve.org/CVERecord?id=CVE-2026-46054 Référence CVE CVE-2026-46056 https://www.cve.org/CVERecord?id=CVE-2026-46056 Référence CVE CVE-2026-46149 https://www.cve.org/CVERecord?id=CVE-2026-46149 Référence CVE CVE-2026-46150 https://www.cve.org/CVERecord?id=CVE-2026-46150 Référence CVE CVE-2026-46266 https://www.cve.org/CVERecord?id=CVE-2026-46266 Référence CVE CVE-2026-46306 https://www.cve.org/CVERecord?id=CVE-2026-46306 Référence CVE CVE-2026-52920 https://www.cve.org/CVERecord?id=CVE-2026-52920 Référence CVE CVE-2026-52924 https://www.cve.org/CVERecord?id=CVE-2026-52924 Référence CVE CVE-2026-52933 https://www.cve.org/CVERecord?id=CVE-2026-52933 Référence CVE CVE-2026-52947 https://www.cve.org/CVERecord?id=CVE-2026-52947 Référence CVE CVE-2026-52971 https://www.cve.org/CVERecord?id=CVE-2026-52971 Référence CVE CVE-2026-53000 https://www.cve.org/CVERecord?id=CVE-2026-53000 Référence CVE CVE-2026-53006 https://www.cve.org/CVERecord?id=CVE-2026-53006 Référence CVE CVE-2026-53016 https://www.cve.org/CVERecord?id=CVE-2026-53016 Référence CVE CVE-2026-53071 https://www.cve.org/CVERecord?id=CVE-2026-53071 Référence CVE CVE-2026-53075 https://www.cve.org/CVERecord?id=CVE-2026-53075 Référence CVE CVE-2026-53131 https://www.cve.org/CVERecord?id=CVE-2026-53131 Référence CVE CVE-2026-53176 https://www.cve.org/CVERecord?id=CVE-2026-53176 Référence CVE CVE-2026-53182 https://www.cve.org/CVERecord?id=CVE-2026-53182 Référence CVE CVE-2026-53192 https://www.cve.org/CVERecord?id=CVE-2026-53192 Référence CVE CVE-2026-53193 https://www.cve.org/CVERecord?id=CVE-2026-53193 Référence CVE CVE-2026-53196 https://www.cve.org/CVERecord?id=CVE-2026-53196 Référence CVE CVE-2026-53223 https://www.cve.org/CVERecord?id=CVE-2026-53223 Référence CVE CVE-2026-53228 https://www.cve.org/CVERecord?id=CVE-2026-53228 Référence CVE CVE-2026-53239 https://www.cve.org/CVERecord?id=CVE-2026-53239 Référence CVE CVE-2026-53246 https://www.cve.org/CVERecord?id=CVE-2026-53246 Référence CVE CVE-2026-53268 https://www.cve.org/CVERecord?id=CVE-2026-53268 Référence CVE CVE-2026-53275 https://www.cve.org/CVERecord?id=CVE-2026-53275 Référence CVE CVE-2026-53361 https://www.cve.org/CVERecord?id=CVE-2026-53361 Référence CVE CVE-2026-63802 https://www.cve.org/CVERecord?id=CVE-2026-63802 Référence CVE CVE-2026-63869 https://www.cve.org/CVERecord?id=CVE-2026-63869 Référence CVE CVE-2026-63886 https://www.cve.org/CVERecord?id=CVE-2026-63886 Référence CVE CVE-2026-63887 https://www.cve.org/CVERecord?id=CVE-2026-63887 Référence CVE CVE-2026-63888 https://www.cve.org/CVERecord?id=CVE-2026-63888 Référence CVE CVE-2026-63889 https://www.cve.org/CVERecord?id=CVE-2026-63889 Référence CVE CVE-2026-63917 https://www.cve.org/CVERecord?id=CVE-2026-63917 Référence CVE CVE-2026-63919 https://www.cve.org/CVERecord?id=CVE-2026-63919 Référence CVE CVE-2026-63921 https://www.cve.org/CVERecord?id=CVE-2026-63921 Référence CVE CVE-2026-63923 https://www.cve.org/CVERecord?id=CVE-2026-63923 Référence CVE CVE-2026-64002 https://www.cve.org/CVERecord?id=CVE-2026-64002 Référence CVE CVE-2026-64015 https://www.cve.org/CVERecord?id=CVE-2026-64015 Référence CVE CVE-2026-64029 https://www.cve.org/CVERecord?id=CVE-2026-64029 Référence CVE CVE-2026-64111 https://www.cve.org/CVERecord?id=CVE-2026-64111 Référence CVE CVE-2026-64117 https://www.cve.org/CVERecord?id=CVE-2026-64117 Référence CVE CVE-2026-64175 https://www.cve.org/CVERecord?id=CVE-2026-64175 Référence CVE CVE-2026-64176 https://www.cve.org/CVERecord?id=CVE-2026-64176 Référence CVE CVE-2026-64268 https://www.cve.org/CVERecord?id=CVE-2026-64268 Référence CVE CVE-2026-64304 https://www.cve.org/CVERecord?id=CVE-2026-64304 Référence CVE CVE-2026-64387 https://www.cve.org/CVERecord?id=CVE-2026-64387 Référence CVE CVE-2026-64414 https://www.cve.org/CVERecord?id=CVE-2026-64414 Référence CVE CVE-2026-64438 https://www.cve.org/CVERecord?id=CVE-2026-64438 Référence CVE CVE-2026-64456 https://www.cve.org/CVERecord?id=CVE-2026-64456 Référence CVE CVE-2026-64530 https://www.cve.org/CVERecord?id=CVE-2026-64530 Référence CVE CVE-2026-68128 https://www.cve.org/CVERecord?id=CVE-2026-68128 Référence CVE CVE-2026-68143 https://www.cve.org/CVERecord?id=CVE-2026-68143 Référence CVE CVE-2026-68200 https://www.cve.org/CVERecord?id=CVE-2026-68200 Référence CVE CVE-2026-68264 https://www.cve.org/CVERecord?id=CVE-2026-68264 Référence CVE CVE-2026-68294 https://www.cve.org/CVERecord?id=CVE-2026-68294 Référence CVE CVE-2026-68363 https://www.cve.org/CVERecord?id=CVE-2026-68363 Référence CVE CVE-2026-68426 https://www.cve.org/CVERecord?id=CVE-2026-68426 Référence CVE CVE-2026-72045 https://www.cve.org/CVERecord?id=CVE-2026-72045 Référence CVE CVE-2026-72098 https://www.cve.org/CVERecord?id=CVE-2026-72098 Référence CVE CVE-2026-72102 https://www.cve.org/CVERecord?id=CVE-2026-72102 Référence CVE CVE-2026-72298 https://www.cve.org/CVERecord?id=CVE-2026-72298 Référence CVE CVE-2026-74480 https://www.cve.org/CVERecord?id=CVE-2026-74480 Référence CVE CVE-2026-74556 https://www.cve.org/CVERecord?id=CVE-2026-74556
No comment yet.
Scooped by Yannick Giquel
September 17, 2:37 PM

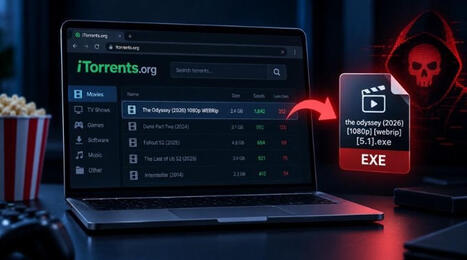
iTorrents.org compromis pour distribuer un malware Windows à la place des films

iTorrents.org compromis pour distribuer un malware Windows à la place des films | Cybersécurité | Scoop.it
Des pirates ont compromis le dépôt itorrents.org pour diffuser MovieReaper, un malware déguisé en films comme The Odyssey. Kaspersky présente cette menace.
No comment yet.
Scooped by Yannick Giquel
September 17, 9:23 AM

Multiples vulnérabilités dans ISC BIND - CERT-FR

Multiples vulnérabilités dans ISC BIND - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Contournement de la politique de sécurité Déni de service à distance Systèmes affectés BIND Supported Preview Edition versions antérieures à 9.20.29-S1 Bind versions 9.21.x antérieures à 9.21.26 Bind versions antérieures à 9.20.29 Résumé De multiples vulnérabilités ont été découvertes dans ISC BIND. Elles permettent à un attaquant de provoquer un déni de service à distance, une atteinte à l'intégrité des données et un contournement de la politique de sécurité. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité ISC BIND cve-2026-75029 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-75029 Bulletin de sécurité ISC BIND cve-2026-76163 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-76163 Bulletin de sécurité ISC BIND cve-2026-77119 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-77119 Bulletin de sécurité ISC BIND cve-2026-77692 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-77692 Bulletin de sécurité ISC BIND cve-2026-78301 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-78301 Bulletin de sécurité ISC BIND cve-2026-80274 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-80274 Bulletin de sécurité ISC BIND cve-2026-81563 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-81563 Bulletin de sécurité ISC BIND cve-2026-81736 du 16 septembre 2026 https://kb.isc.org/v1/docs/cve-2026-81736 Référence CVE CVE-2026-75029 https://www.cve.org/CVERecord?id=CVE-2026-75029 Référence CVE CVE-2026-76163 https://www.cve.org/CVERecord?id=CVE-2026-76163 Référence CVE CVE-2026-77119 https://www.cve.org/CVERecord?id=CVE-2026-77119 Référence CVE CVE-2026-77692 https://www.cve.org/CVERecord?id=CVE-2026-77692 Référence CVE CVE-2026-78301 https://www.cve.org/CVERecord?id=CVE-2026-78301 Référence CVE CVE-2026-80274 https://www.cve.org/CVERecord?id=CVE-2026-80274 Référence CVE CVE-2026-81563 https://www.cve.org/CVERecord?id=CVE-2026-81563 Référence CVE CVE-2026-81736 https://www.cve.org/CVERecord?id=CVE-2026-81736
No comment yet.
Scooped by Yannick Giquel
September 17, 9:23 AM

Multiples vulnérabilités dans Drupal - CERT-FR

Multiples vulnérabilités dans Drupal - CERT-FR | Cybersécurité | Scoop.it
Risque Injection de code indirecte à distance (XSS) Systèmes affectés Drupal versions 11.4.x antérieures à 11.4.7 Drupal versions 11.x antérieures à 11.3.17 Drupal versions antérieures à 10.6.17 Résumé De multiples vulnérabilités ont été découvertes dans Drupal. Elles permettent à un attaquant de provoquer une injection de code indirecte à distance (XSS). Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Drupal SA-CORE-2026-013 du 16 septembre 2026 https://drupal.org/sa-core-2026-013
No comment yet.
Scooped by Yannick Giquel
September 16, 6:09 PM

Sébastien Giai-Checa, directeur Cybersécurité, SCC France : « Cyb ...

Sébastien Giai-Checa, directeur Cybersécurité, SCC France : « Cyb ... | Cybersécurité | Scoop.it
Pendant longtemps, la cybersécurité a été pensée comme une course à l'armement technologique : multiplier les solutions de protection, renforcer les pare-feu, déployer de nouveaux outils de détection.
No comment yet.
Scooped by Yannick Giquel
September 16, 8:09 AM

Multiples vulnérabilités dans Mattermost Server - CERT-FR

Multiples vulnérabilités dans Mattermost Server - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à la confidentialité des données Non spécifié par l'éditeur Systèmes affectés Mattermost Server versions 11.10.x antérieures à 11.10.2 Mattermost Server versions 11.7.x antérieures à 11.7.11 Mattermost Server versions 11.8.x antérieures à 11.8.6 Mattermost Server versions 11.9.x antérieures à 11.9.2 Mattermost Server versions antérieures à 10.11.23 Résumé De multiples vulnérabilités ont été découvertes dans Mattermost Server. Elles permettent à un attaquant de provoquer une atteinte à la confidentialité des données et un problème de sécurité non spécifié par l'éditeur. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Mattermost MMSA-2026-00702 du 14 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00711 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00726 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00727 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00747 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00748 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00752 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00754 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00756 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00757 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00758 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00761 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00763 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00764 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00765 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00766 du 15 septembre 2026 https://mattermost.com/security-updates/ Bulletin de sécurité Mattermost MMSA-2026-00773 du 15 septembre 2026 https://mattermost.com/security-updates/ Référence CVE CVE-2026-91181 https://www.cve.org/CVERecord?id=CVE-2026-91181
No comment yet.
Scooped by Yannick Giquel
September 15, 3:53 PM

Agents autonomes, responsabilité introuvable : le paradoxe silencieux qui s’installe au cœur de la cybersécurité

Agents autonomes, responsabilité introuvable : le paradoxe silencieux qui s’installe au cœur de la cybersécurité | Cybersécurité | Scoop.it
No comment yet.
Scooped by Yannick Giquel
September 15, 4:37 AM

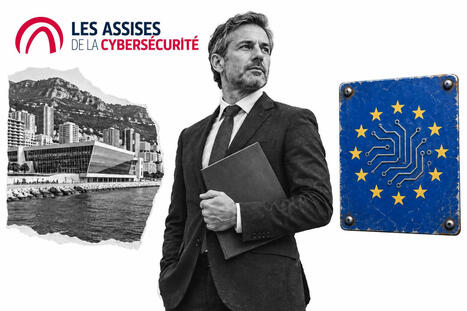
Les Assises de la cybersécurité ouvriront leurs portes le 7 octobre, sous le signe du CRA et du post-quantique

Les Assises de la cybersécurité ouvriront leurs portes le 7 octobre, sous le signe du CRA et du post-quantique | Cybersécurité | Scoop.it
Les Assises de la cybersécurité ont retenu « Osons ! » comme mot d’ordre de leur 26e édition, du 7 au 10 octobre à Monaco.Un appel au volontarisme décomplexé, et les organisateurs veulent rendre la fonction du RSSI visible et influente dans l’entreprise, un an après une édition 2025 ouverte dans ...
No comment yet.
Scooped by Yannick Giquel
September 14, 11:08 AM

Multiples vulnérabilités dans Microsoft Edge - CERT-FR

Multiples vulnérabilités dans Microsoft Edge - CERT-FR | Cybersécurité | Scoop.it
Risques Contournement de la politique de sécurité Non spécifié par l'éditeur Systèmes affectés Microsoft Edge versions antérieures à 151.0.4129.107 Microsoft Edge versions antérieures à 152.0.4191.66 Résumé De multiples vulnérabilités ont été découvertes dans Microsoft Edge. Elles permettent à un attaquant de provoquer un contournement de la politique de sécurité et un problème de sécurité non spécifié par l'éditeur. Microsoft indique que la vulnérabilité CVE-2026-87491 est activement exploitée. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Microsoft Edge CVE-2026-76017 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76017 Bulletin de sécurité Microsoft Edge CVE-2026-76018 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76018 Bulletin de sécurité Microsoft Edge CVE-2026-76019 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76019 Bulletin de sécurité Microsoft Edge CVE-2026-76021 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76021 Bulletin de sécurité Microsoft Edge CVE-2026-76022 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76022 Bulletin de sécurité Microsoft Edge CVE-2026-76023 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76023 Bulletin de sécurité Microsoft Edge CVE-2026-76036 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76036 Bulletin de sécurité Microsoft Edge CVE-2026-76039 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-76039 Bulletin de sécurité Microsoft Edge CVE-2026-77490 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-77490 Bulletin de sécurité Microsoft Edge CVE-2026-84330 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-84330 Bulletin de sécurité Microsoft Edge CVE-2026-84333 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-84333 Bulletin de sécurité Microsoft Edge CVE-2026-84352 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-84352 Bulletin de sécurité Microsoft Edge CVE-2026-85042 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85042 Bulletin de sécurité Microsoft Edge CVE-2026-85043 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85043 Bulletin de sécurité Microsoft Edge CVE-2026-85045 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85045 Bulletin de sécurité Microsoft Edge CVE-2026-85048 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85048 Bulletin de sécurité Microsoft Edge CVE-2026-85049 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85049 Bulletin de sécurité Microsoft Edge CVE-2026-85051 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85051 Bulletin de sécurité Microsoft Edge CVE-2026-85052 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85052 Bulletin de sécurité Microsoft Edge CVE-2026-85053 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-85053 Bulletin de sécurité Microsoft Edge CVE-2026-87491 du 11 septembre 2026 https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-87491 Référence CVE CVE-2026-76017 https://www.cve.org/CVERecord?id=CVE-2026-76017 Référence CVE CVE-2026-76018 https://www.cve.org/CVERecord?id=CVE-2026-76018 Référence CVE CVE-2026-76019 https://www.cve.org/CVERecord?id=CVE-2026-76019 Référence CVE CVE-2026-76021 https://www.cve.org/CVERecord?id=CVE-2026-76021 Référence CVE CVE-2026-76022 https://www.cve.org/CVERecord?id=CVE-2026-76022 Référence CVE CVE-2026-76023 https://www.cve.org/CVERecord?id=CVE-2026-76023 Référence CVE CVE-2026-76036 https://www.cve.org/CVERecord?id=CVE-2026-76036 Référence CVE CVE-2026-76039 https://www.cve.org/CVERecord?id=CVE-2026-76039 Référence CVE CVE-2026-77490 https://www.cve.org/CVERecord?id=CVE-2026-77490 Référence CVE CVE-2026-84330 https://www.cve.org/CVERecord?id=CVE-2026-84330 Référence CVE CVE-2026-84333 https://www.cve.org/CVERecord?id=CVE-2026-84333 Référence CVE CVE-2026-84352 https://www.cve.org/CVERecord?id=CVE-2026-84352 Référence CVE CVE-2026-85042 https://www.cve.org/CVERecord?id=CVE-2026-85042 Référence CVE CVE-2026-85043 https://www.cve.org/CVERecord?id=CVE-2026-85043 Référence CVE CVE-2026-85045 https://www.cve.org/CVERecord?id=CVE-2026-85045 Référence CVE CVE-2026-85048 https://www.cve.org/CVERecord?id=CVE-2026-85048 Référence CVE CVE-2026-85049 https://www.cve.org/CVERecord?id=CVE-2026-85049 Référence CVE CVE-2026-85051 https://www.cve.org/CVERecord?id=CVE-2026-85051 Référence CVE CVE-2026-85052 https://www.cve.org/CVERecord?id=CVE-2026-85052 Référence CVE CVE-2026-85053 https://www.cve.org/CVERecord?id=CVE-2026-85053 Référence CVE CVE-2026-87491 https://www.cve.org/CVERecord?id=CVE-2026-87491
No comment yet.
Scooped by Yannick Giquel
September 13, 11:23 AM

Vulnérabilités : l’écosystème open source face aux dilemmes du tout IA

Vulnérabilités : l’écosystème open source face aux dilemmes du tout IA | Cybersécurité | Scoop.it
L’IA générative bouscule les pratiques de détection de vulnérabilités et de découvertes de failles dans les projets open source. Après des rapports de piètre qualité en 2025, puis des scans « en profondeur » prometteurs, mainteneurs et fondations cherchent désormais le bon équilibre pour renforcer la sécurité de leur projet sans crouler sous la charge de travail. Au vu des gains déjà tangibles, un débat émerge au sein de l’Eclipse Foundation : faut-il imposer l’usage de l’IA pour la sécurité ? > Lire l’article de Gaétan Raoul Les dessins du MagIT Comment les agents d’OpenAI ont détourné un wiki Devant le juge, qui est responsable des erreurs de l’IA ? Rachat d’Hugging Face : Nvidia confirme l’accord à 12,93 milliards de dollars Voir tous les dessins
No comment yet.
Scooped by Yannick Giquel
September 11, 1:08 PM

Cybersécurité : l’âge de l’industrialisation, selon Anthropic

Cybersécurité : l’âge de l’industrialisation, selon Anthropic | Cybersécurité | Scoop.it
Anthropic a publié ce 10 septembre un nouveau rapport de renseignement sur les menaces, le quatrième de son histoire.L’entreprise y précise la manière…...
No comment yet.
Scooped by Yannick Giquel
September 11, 6:53 AM

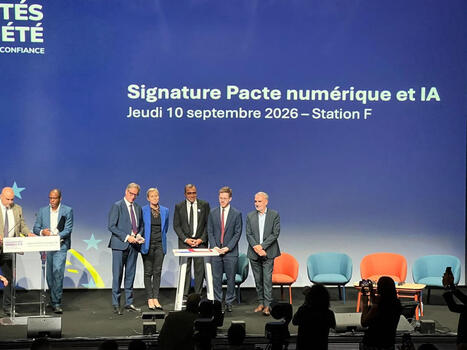
Cloud, IA, cybersécurité : l'État fait un pas vers la filière française

Cloud, IA, cybersécurité : l'État fait un pas vers la filière française | Cybersécurité | Scoop.it
Cloud, IA, cybersécurité : l'État fait un pas vers la filière française.
No comment yet.
Scooped by Yannick Giquel
September 18, 11:09 AM

Multiples vulnérabilités dans les produits IBM - CERT-FR

Multiples vulnérabilités dans les produits IBM - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Exécution de code arbitraire à distance Falsification de requêtes côté serveur (SSRF) Injection de code indirecte à distance (XSS) Non spécifié par l'éditeur Élévation de privilèges Systèmes affectés AIX version 7.2 sans les derniers correctifs de sécurité AIX version 7.3 sans les derniers correctifs de sécurité Cognos Analytics versions 12.0.x antérieures à 12.0.4 FP3 Cognos Analytics versions 12.1.x antérieures à 12.1.3 FP2 Db2 Developer Extension version 1.1.2 antérieure à 1.2.0 Db2 versions 11.5.x antérieures à 11.5.9 sans le dernier correctif de sécurité Db2 versions 12.1.x antérieures à 12.1.4 sans le dernier correctif de sécurité Db2 versions 12.1.x antérieures à 12.1.5 sans le dernier correctif de sécurité Informix Dynamic Server version 12.10 avec IBM InformixHQ versions antérieure à 3.3.2 Informix Dynamic Server versions 14.10.x antérieures à 14.10.xC14 Informix Dynamic Server versions 15.0.x antérieures à 15.0.1.14 Security SOAR versions 51.0.x antérieures à 51.0.11.1 SOAR QRadar Plugin App version 5.3.1 antérieure à 5.7.0 Sterling B2B Integrator versions 6.2.2.x antérieures à 6.2.2.1_1 Sterling B2B Integrator versions 6.2.x antérieures à 6.2.1.2_1 Sterling Connect:Direct FTP+ versions 1.3.x antérieures à 1.3.0.6 Sterling File Gateway versions 6.2.2.x antérieures à 6.2.2.1_1 Sterling File Gateway versions 6.2.x antérieures à 6.2.1.2_1 Sterling Partner Engagement Manager Essentials Edition versions 6.2.4.x antérieures à 6.2.4.5 Sterling Partner Engagement Manager Essentials Edition versions 6.3.x antérieures à 6.3.0.3 Sterling Partner Engagement Manager Standard Edition versions 6.2.4.x antérieures à 6.2.4.5 Sterling Secure Proxy versions 6.1.0.x antérieures à 6.1.0.4 iFix01 Sterling Secure Proxy versions 6.2.1.x antérieures à 6.2.1.3 Tivoli Application Dependency Discovery Manager versions 7.3.x sans le dernier correctif de sécurité VIOS version 4.1 sans les derniers correctifs de sécurité WebSphere Application Server - Liberty versions 17.0.0.3 à 26.0.0.9 sans le dernier correctif de sécurité ou antérieures à 26.0.0.10 (disponibilité prévue pour le dernier trimestre 2026) WebSphere Hybrid Edition version 5.1 sans les derniers correctifs de sécurité Résumé De multiples vulnérabilités ont été découvertes dans les produits IBM. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire à distance, une élévation de privilèges et un déni de service à distance. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité IBM 7287180 du 11 septembre 2026 https://www.ibm.com/support/pages/node/7287180 Bulletin de sécurité IBM 7287209 du 11 septembre 2026 https://www.ibm.com/support/pages/node/7287209 Bulletin de sécurité IBM 7287211 du 11 septembre 2026 https://www.ibm.com/support/pages/node/7287211 Bulletin de sécurité IBM 7286659 du 14 septembre 2026 https://www.ibm.com/support/pages/node/7286659 Bulletin de sécurité IBM 7287327 du 14 septembre 2026 https://www.ibm.com/support/pages/node/7287327 Bulletin de sécurité IBM 7287367 du 14 septembre 2026 https://www.ibm.com/support/pages/node/7287367 Bulletin de sécurité IBM 7287370 du 14 septembre 2026 https://www.ibm.com/support/pages/node/7287370 Bulletin de sécurité IBM 7287496 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287496 Bulletin de sécurité IBM 7287497 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287497 Bulletin de sécurité IBM 7287498 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287498 Bulletin de sécurité IBM 7287500 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287500 Bulletin de sécurité IBM 7287501 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287501 Bulletin de sécurité IBM 7287503 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287503 Bulletin de sécurité IBM 7287514 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287514 Bulletin de sécurité IBM 7287516 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287516 Bulletin de sécurité IBM 7287519 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287519 Bulletin de sécurité IBM 7287520 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287520 Bulletin de sécurité IBM 7287544 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287544 Bulletin de sécurité IBM 7287612 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287612 Bulletin de sécurité IBM 7287632 du 15 septembre 2026 https://www.ibm.com/support/pages/node/7287632 Bulletin de sécurité IBM 7286987 du 16 septembre 2026 https://www.ibm.com/support/pages/node/7286987 Bulletin de sécurité IBM 7287477 du 16 septembre 2026 https://www.ibm.com/support/pages/node/7287477 Bulletin de sécurité IBM 7287795 du 16 septembre 2026 https://www.ibm.com/support/pages/node/7287795 Bulletin de sécurité IBM 7287885 du 16 septembre 2026 https://www.ibm.com/support/pages/node/7287885 Bulletin de sécurité IBM 7287917 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287917 Bulletin de sécurité IBM 7287954 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287954 Bulletin de sécurité IBM 7287956 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287956 Bulletin de sécurité IBM 7287957 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287957 Bulletin de sécurité IBM 7287958 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287958 Bulletin de sécurité IBM 7287959 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287959 Bulletin de sécurité IBM 7287962 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7287962 Bulletin de sécurité IBM 7288068 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288068 Bulletin de sécurité IBM 7288075 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288075 Bulletin de sécurité IBM 7288077 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288077 Bulletin de sécurité IBM 7288078 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288078 Bulletin de sécurité IBM 7288080 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288080 Bulletin de sécurité IBM 7288086 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288086 Bulletin de sécurité IBM 7288092 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288092 Bulletin de sécurité IBM 7288365 du 17 septembre 2026 https://www.ibm.com/support/pages/node/7288365 Référence CVE CVE-2017-16026 https://www.cve.org/CVERecord?id=CVE-2017-16026 Référence CVE CVE-2021-23336 https://www.cve.org/CVERecord?id=CVE-2021-23336 Référence CVE CVE-2021-23337 https://www.cve.org/CVERecord?id=CVE-2021-23337 Référence CVE CVE-2022-42969 https://www.cve.org/CVERecord?id=CVE-2022-42969 Référence CVE CVE-2023-1370 https://www.cve.org/CVERecord?id=CVE-2023-1370 Référence CVE CVE-2023-28155 https://www.cve.org/CVERecord?id=CVE-2023-28155 Référence CVE CVE-2023-44487 https://www.cve.org/CVERecord?id=CVE-2023-44487 Référence CVE CVE-2024-47535 https://www.cve.org/CVERecord?id=CVE-2024-47535 Référence CVE CVE-2024-47764 https://www.cve.org/CVERecord?id=CVE-2024-47764 Référence CVE CVE-2024-56344 https://www.cve.org/CVERecord?id=CVE-2024-56344 Référence CVE CVE-2024-57699 https://www.cve.org/CVERecord?id=CVE-2024-57699 Référence CVE CVE-2025-12635 https://www.cve.org/CVERecord?id=CVE-2025-12635 Référence CVE CVE-2025-13465 https://www.cve.org/CVERecord?id=CVE-2025-13465 Référence CVE CVE-2025-13882 https://www.cve.org/CVERecord?id=CVE-2025-13882 Référence CVE CVE-2025-14009 https://www.cve.org/CVERecord?id=CVE-2025-14009 Référence CVE CVE-2025-14549 https://www.cve.org/CVERecord?id=CVE-2025-14549 Référence CVE CVE-2025-14915 https://www.cve.org/CVERecord?id=CVE-2025-14915 Référence CVE CVE-2025-14923 https://www.cve.org/CVERecord?id=CVE-2025-14923 Référence CVE CVE-2025-33123 https://www.cve.org/CVERecord?id=CVE-2025-33123 Référence CVE CVE-2025-33147 https://www.cve.org/CVERecord?id=CVE-2025-33147 Référence CVE CVE-2025-36076 https://www.cve.org/CVERecord?id=CVE-2025-36076 Référence CVE CVE-2025-4517 https://www.cve.org/CVERecord?id=CVE-2025-4517 Référence CVE CVE-2025-59375 https://www.cve.org/CVERecord?id=CVE-2025-59375 Référence CVE CVE-2025-62718 https://www.cve.org/CVERecord?id=CVE-2025-62718 Référence CVE CVE-2025-68161 https://www.cve.org/CVERecord?id=CVE-2025-68161 Référence CVE CVE-2025-69534 https://www.cve.org/CVERecord?id=CVE-2025-69534 Référence CVE CVE-2025-8885 https://www.cve.org/CVERecord?id=CVE-2025-8885 Référence CVE CVE-2025-9095 https://www.cve.org/CVERecord?id=CVE-2025-9095 Référence CVE CVE-2025-9096 https://www.cve.org/CVERecord?id=CVE-2025-9096 Référence CVE CVE-2026-0846 https://www.cve.org/CVERecord?id=CVE-2026-0846 Référence CVE CVE-2026-0847 https://www.cve.org/CVERecord?id=CVE-2026-0847 Référence CVE CVE-2026-0848 https://www.cve.org/CVERecord?id=CVE-2026-0848 Référence CVE CVE-2026-10050 https://www.cve.org/CVERecord?id=CVE-2026-10050 Référence CVE CVE-2026-10051 https://www.cve.org/CVERecord?id=CVE-2026-10051 Référence CVE CVE-2026-10541 https://www.cve.org/CVERecord?id=CVE-2026-10541 Référence CVE CVE-2026-10723 https://www.cve.org/CVERecord?id=CVE-2026-10723 Référence CVE CVE-2026-10822 https://www.cve.org/CVERecord?id=CVE-2026-10822 Référence CVE CVE-2026-10841 https://www.cve.org/CVERecord?id=CVE-2026-10841 Référence CVE CVE-2026-10842 https://www.cve.org/CVERecord?id=CVE-2026-10842 Référence CVE CVE-2026-11331 https://www.cve.org/CVERecord?id=CVE-2026-11331 Référence CVE CVE-2026-11541 https://www.cve.org/CVERecord?id=CVE-2026-11541 Référence CVE CVE-2026-11548 https://www.cve.org/CVERecord?id=CVE-2026-11548 Référence CVE CVE-2026-11549 https://www.cve.org/CVERecord?id=CVE-2026-11549 Référence CVE CVE-2026-11622 https://www.cve.org/CVERecord?id=CVE-2026-11622 Référence CVE CVE-2026-11721 https://www.cve.org/CVERecord?id=CVE-2026-11721 Référence CVE CVE-2026-11722 https://www.cve.org/CVERecord?id=CVE-2026-11722 Référence CVE CVE-2026-11897 https://www.cve.org/CVERecord?id=CVE-2026-11897 Référence CVE CVE-2026-12143 https://www.cve.org/CVERecord?id=CVE-2026-12143 Référence CVE CVE-2026-12243 https://www.cve.org/CVERecord?id=CVE-2026-12243 Référence CVE CVE-2026-12617 https://www.cve.org/CVERecord?id=CVE-2026-12617 Référence CVE CVE-2026-13204 https://www.cve.org/CVERecord?id=CVE-2026-13204 Référence CVE CVE-2026-13321 https://www.cve.org/CVERecord?id=CVE-2026-13321 Référence CVE CVE-2026-14257 https://www.cve.org/CVERecord?id=CVE-2026-14257 Référence CVE CVE-2026-14742 https://www.cve.org/CVERecord?id=CVE-2026-14742 Référence CVE CVE-2026-14981 https://www.cve.org/CVERecord?id=CVE-2026-14981 Référence CVE CVE-2026-15057 https://www.cve.org/CVERecord?id=CVE-2026-15057 Référence CVE CVE-2026-15064 https://www.cve.org/CVERecord?id=CVE-2026-15064 Référence CVE CVE-2026-15325 https://www.cve.org/CVERecord?id=CVE-2026-15325 Référence CVE CVE-2026-15328 https://www.cve.org/CVERecord?id=CVE-2026-15328 Référence CVE CVE-2026-15396 https://www.cve.org/CVERecord?id=CVE-2026-15396 Référence CVE CVE-2026-15412 https://www.cve.org/CVERecord?id=CVE-2026-15412 Référence CVE CVE-2026-1561 https://www.cve.org/CVERecord?id=CVE-2026-1561 Référence CVE CVE-2026-15634 https://www.cve.org/CVERecord?id=CVE-2026-15634 Référence CVE CVE-2026-16243 https://www.cve.org/CVERecord?id=CVE-2026-16243 Référence CVE CVE-2026-16439 https://www.cve.org/CVERecord?id=CVE-2026-16439 Référence CVE CVE-2026-16441 https://www.cve.org/CVERecord?id=CVE-2026-16441 Référence CVE CVE-2026-19290 https://www.cve.org/CVERecord?id=CVE-2026-19290 Référence CVE CVE-2026-22007 https://www.cve.org/CVERecord?id=CVE-2026-22007 Référence CVE CVE-2026-22008 https://www.cve.org/CVERecord?id=CVE-2026-22008 Référence CVE CVE-2026-22013 https://www.cve.org/CVERecord?id=CVE-2026-22013 Référence CVE CVE-2026-22016 https://www.cve.org/CVERecord?id=CVE-2026-22016 Référence CVE CVE-2026-22018 https://www.cve.org/CVERecord?id=CVE-2026-22018 Référence CVE CVE-2026-22021 https://www.cve.org/CVERecord?id=CVE-2026-22021 Référence CVE CVE-2026-22741 https://www.cve.org/CVERecord?id=CVE-2026-22741 Référence CVE CVE-2026-22745 https://www.cve.org/CVERecord?id=CVE-2026-22745 Référence CVE CVE-2026-22746 https://www.cve.org/CVERecord?id=CVE-2026-22746 Référence CVE CVE-2026-22751 https://www.cve.org/CVERecord?id=CVE-2026-22751 Référence CVE CVE-2026-23490 https://www.cve.org/CVERecord?id=CVE-2026-23490 Référence CVE CVE-2026-23865 https://www.cve.org/CVERecord?id=CVE-2026-23865 Référence CVE CVE-2026-24051 https://www.cve.org/CVERecord?id=CVE-2026-24051 Référence CVE CVE-2026-25639 https://www.cve.org/CVERecord?id=CVE-2026-25639 Référence CVE CVE-2026-25646 https://www.cve.org/CVERecord?id=CVE-2026-25646 Référence CVE CVE-2026-26007 https://www.cve.org/CVERecord?id=CVE-2026-26007 Référence CVE CVE-2026-26996 https://www.cve.org/CVERecord?id=CVE-2026-26996 Référence CVE CVE-2026-27024 https://www.cve.org/CVERecord?id=CVE-2026-27024 Référence CVE CVE-2026-27025 https://www.cve.org/CVERecord?id=CVE-2026-27025 Référence CVE CVE-2026-27026 https://www.cve.org/CVERecord?id=CVE-2026-27026 Référence CVE CVE-2026-27205 https://www.cve.org/CVERecord?id=CVE-2026-27205 Référence CVE CVE-2026-27903 https://www.cve.org/CVERecord?id=CVE-2026-27903 Référence CVE CVE-2026-27904 https://www.cve.org/CVERecord?id=CVE-2026-27904 Référence CVE CVE-2026-2950 https://www.cve.org/CVERecord?id=CVE-2026-2950 Référence CVE CVE-2026-30922 https://www.cve.org/CVERecord?id=CVE-2026-30922 Référence CVE CVE-2026-31958 https://www.cve.org/CVERecord?id=CVE-2026-31958 Référence CVE CVE-2026-33230 https://www.cve.org/CVERecord?id=CVE-2026-33230 Référence CVE CVE-2026-33231 https://www.cve.org/CVERecord?id=CVE-2026-33231 Référence CVE CVE-2026-33236 https://www.cve.org/CVERecord?id=CVE-2026-33236 Référence CVE CVE-2026-33416 https://www.cve.org/CVERecord?id=CVE-2026-33416 Référence CVE CVE-2026-34073 https://www.cve.org/CVERecord?id=CVE-2026-34073 Référence CVE CVE-2026-34197 https://www.cve.org/CVERecord?id=CVE-2026-34197 Référence CVE CVE-2026-34268 https://www.cve.org/CVERecord?id=CVE-2026-34268 Référence CVE CVE-2026-34282 https://www.cve.org/CVERecord?id=CVE-2026-34282 Référence CVE CVE-2026-34477 https://www.cve.org/CVERecord?id=CVE-2026-34477 Référence CVE CVE-2026-34478 https://www.cve.org/CVERecord?id=CVE-2026-34478 Référence CVE CVE-2026-34479 https://www.cve.org/CVERecord?id=CVE-2026-34479 Référence CVE CVE-2026-34480 https://www.cve.org/CVERecord?id=CVE-2026-34480 Référence CVE CVE-2026-34481 https://www.cve.org/CVERecord?id=CVE-2026-34481 Référence CVE CVE-2026-35536 https://www.cve.org/CVERecord?id=CVE-2026-35536 Référence CVE CVE-2026-3621 https://www.cve.org/CVERecord?id=CVE-2026-3621 Référence CVE CVE-2026-3713 https://www.cve.org/CVERecord?id=CVE-2026-3713 Référence CVE CVE-2026-39824 https://www.cve.org/CVERecord?id=CVE-2026-39824 Référence CVE CVE-2026-39892 https://www.cve.org/CVERecord?id=CVE-2026-39892 Référence CVE CVE-2026-40175 https://www.cve.org/CVERecord?id=CVE-2026-40175 Référence CVE CVE-2026-40192 https://www.cve.org/CVERecord?id=CVE-2026-40192 Référence CVE CVE-2026-40466 https://www.cve.org/CVERecord?id=CVE-2026-40466 Référence CVE CVE-2026-40682 https://www.cve.org/CVERecord?id=CVE-2026-40682 Référence CVE CVE-2026-40864 https://www.cve.org/CVERecord?id=CVE-2026-40864 Référence CVE CVE-2026-40973 https://www.cve.org/CVERecord?id=CVE-2026-40973 Référence CVE CVE-2026-40988 https://www.cve.org/CVERecord?id=CVE-2026-40988 Référence CVE CVE-2026-40999 https://www.cve.org/CVERecord?id=CVE-2026-40999 Référence CVE CVE-2026-41006 https://www.cve.org/CVERecord?id=CVE-2026-41006 Référence CVE CVE-2026-41007 https://www.cve.org/CVERecord?id=CVE-2026-41007 Référence CVE CVE-2026-41044 https://www.cve.org/CVERecord?id=CVE-2026-41044 Référence CVE CVE-2026-41254 https://www.cve.org/CVERecord?id=CVE-2026-41254 Référence CVE CVE-2026-41417 https://www.cve.org/CVERecord?id=CVE-2026-41417 Référence CVE CVE-2026-41603 https://www.cve.org/CVERecord?id=CVE-2026-41603 Référence CVE CVE-2026-41715 https://www.cve.org/CVERecord?id=CVE-2026-41715 Référence CVE CVE-2026-41839 https://www.cve.org/CVERecord?id=CVE-2026-41839 Référence CVE CVE-2026-41840 https://www.cve.org/CVERecord?id=CVE-2026-41840 Référence CVE CVE-2026-41841 https://www.cve.org/CVERecord?id=CVE-2026-41841 Référence CVE CVE-2026-41842 https://www.cve.org/CVERecord?id=CVE-2026-41842 Référence CVE CVE-2026-41843 https://www.cve.org/CVERecord?id=CVE-2026-41843 Référence CVE CVE-2026-41844 https://www.cve.org/CVERecord?id=CVE-2026-41844 Référence CVE CVE-2026-41845 https://www.cve.org/CVERecord?id=CVE-2026-41845 Référence CVE CVE-2026-41846 https://www.cve.org/CVERecord?id=CVE-2026-41846 Référence CVE CVE-2026-41848 https://www.cve.org/CVERecord?id=CVE-2026-41848 Référence CVE CVE-2026-41850 https://www.cve.org/CVERecord?id=CVE-2026-41850 Référence CVE CVE-2026-41851 https://www.cve.org/CVERecord?id=CVE-2026-41851 Référence CVE CVE-2026-41852 https://www.cve.org/CVERecord?id=CVE-2026-41852 Référence CVE CVE-2026-41853 https://www.cve.org/CVERecord?id=CVE-2026-41853 Référence CVE CVE-2026-41854 https://www.cve.org/CVERecord?id=CVE-2026-41854 Référence CVE CVE-2026-41907 https://www.cve.org/CVERecord?id=CVE-2026-41907 Référence CVE CVE-2026-41988 https://www.cve.org/CVERecord?id=CVE-2026-41988 Référence CVE CVE-2026-42027 https://www.cve.org/CVERecord?id=CVE-2026-42027 Référence CVE CVE-2026-42033 https://www.cve.org/CVERecord?id=CVE-2026-42033 Référence CVE CVE-2026-42034 https://www.cve.org/CVERecord?id=CVE-2026-42034 Référence CVE CVE-2026-42035 https://www.cve.org/CVERecord?id=CVE-2026-42035 Référence CVE CVE-2026-42036 https://www.cve.org/CVERecord?id=CVE-2026-42036 Référence CVE CVE-2026-42037 https://www.cve.org/CVERecord?id=CVE-2026-42037 Référence CVE CVE-2026-42038 https://www.cve.org/CVERecord?id=CVE-2026-42038 Référence CVE CVE-2026-42039 https://www.cve.org/CVERecord?id=CVE-2026-42039 Référence CVE CVE-2026-42040 https://www.cve.org/CVERecord?id=CVE-2026-42040 Référence CVE CVE-2026-42041 https://www.cve.org/CVERecord?id=CVE-2026-42041 Référence CVE CVE-2026-42042 https://www.cve.org/CVERecord?id=CVE-2026-42042 Référence CVE CVE-2026-42043 https://www.cve.org/CVERecord?id=CVE-2026-42043 Référence CVE CVE-2026-42044 https://www.cve.org/CVERecord?id=CVE-2026-42044 Référence CVE CVE-2026-42198 https://www.cve.org/CVERecord?id=CVE-2026-42198 Référence CVE CVE-2026-42264 https://www.cve.org/CVERecord?id=CVE-2026-42264 Référence CVE CVE-2026-42402 https://www.cve.org/CVERecord?id=CVE-2026-42402 Référence CVE CVE-2026-42403 https://www.cve.org/CVERecord?id=CVE-2026-42403 Référence CVE CVE-2026-42404 https://www.cve.org/CVERecord?id=CVE-2026-42404 Référence CVE CVE-2026-42440 https://www.cve.org/CVERecord?id=CVE-2026-42440 Référence CVE CVE-2026-42577 https://www.cve.org/CVERecord?id=CVE-2026-42577 Référence CVE CVE-2026-42578 https://www.cve.org/CVERecord?id=CVE-2026-42578 Référence CVE CVE-2026-42579 https://www.cve.org/CVERecord?id=CVE-2026-42579 Référence CVE CVE-2026-42580 https://www.cve.org/CVERecord?id=CVE-2026-42580 Référence CVE CVE-2026-42581 https://www.cve.org/CVERecord?id=CVE-2026-42581 Référence CVE CVE-2026-42583 https://www.cve.org/CVERecord?id=CVE-2026-42583 Référence CVE CVE-2026-42584 https://www.cve.org/CVERecord?id=CVE-2026-42584 Référence CVE CVE-2026-42585 https://www.cve.org/CVERecord?id=CVE-2026-42585 Référence CVE CVE-2026-42586 https://www.cve.org/CVERecord?id=CVE-2026-42586 Référence CVE CVE-2026-42587 https://www.cve.org/CVERecord?id=CVE-2026-42587 Référence CVE CVE-2026-43827 https://www.cve.org/CVERecord?id=CVE-2026-43827 Référence CVE CVE-2026-43828 https://www.cve.org/CVERecord?id=CVE-2026-43828 Référence CVE CVE-2026-43869 https://www.cve.org/CVERecord?id=CVE-2026-43869 Référence CVE CVE-2026-4410 https://www.cve.org/CVERecord?id=CVE-2026-4410 Référence CVE CVE-2026-44248 https://www.cve.org/CVERecord?id=CVE-2026-44248 Référence CVE CVE-2026-44249 https://www.cve.org/CVERecord?id=CVE-2026-44249 Référence CVE CVE-2026-44250 https://www.cve.org/CVERecord?id=CVE-2026-44250 Référence CVE CVE-2026-44431 https://www.cve.org/CVERecord?id=CVE-2026-44431 Référence CVE CVE-2026-44432 https://www.cve.org/CVERecord?id=CVE-2026-44432 Référence CVE CVE-2026-44890 https://www.cve.org/CVERecord?id=CVE-2026-44890 Référence CVE CVE-2026-44893 https://www.cve.org/CVERecord?id=CVE-2026-44893 Référence CVE CVE-2026-45205 https://www.cve.org/CVERecord?id=CVE-2026-45205 Référence CVE CVE-2026-4539 https://www.cve.org/CVERecord?id=CVE-2026-4539 Référence CVE CVE-2026-45416 https://www.cve.org/CVERecord?id=CVE-2026-45416 Référence CVE CVE-2026-45536 https://www.cve.org/CVERecord?id=CVE-2026-45536 Référence CVE CVE-2026-46917 https://www.cve.org/CVERecord?id=CVE-2026-46917 Référence CVE CVE-2026-46968 https://www.cve.org/CVERecord?id=CVE-2026-46968 Référence CVE CVE-2026-47010 https://www.cve.org/CVERecord?id=CVE-2026-47010 Référence CVE CVE-2026-47021 https://www.cve.org/CVERecord?id=CVE-2026-47021 Référence CVE CVE-2026-47027 https://www.cve.org/CVERecord?id=CVE-2026-47027 Référence CVE CVE-2026-47057 https://www.cve.org/CVERecord?id=CVE-2026-47057 Référence CVE CVE-2026-47058 https://www.cve.org/CVERecord?id=CVE-2026-47058 Référence CVE CVE-2026-47059 https://www.cve.org/CVERecord?id=CVE-2026-47059 Référence CVE CVE-2026-47063 https://www.cve.org/CVERecord?id=CVE-2026-47063 Référence CVE CVE-2026-47065 https://www.cve.org/CVERecord?id=CVE-2026-47065 Référence CVE CVE-2026-47244 https://www.cve.org/CVERecord?id=CVE-2026-47244 Référence CVE CVE-2026-47838 https://www.cve.org/CVERecord?id=CVE-2026-47838 Référence CVE CVE-2026-4800 https://www.cve.org/CVERecord?id=CVE-2026-4800 Référence CVE CVE-2026-48006 https://www.cve.org/CVERecord?id=CVE-2026-48006 Référence CVE CVE-2026-48043 https://www.cve.org/CVERecord?id=CVE-2026-48043 Référence CVE CVE-2026-48059 https://www.cve.org/CVERecord?id=CVE-2026-48059 Référence CVE CVE-2026-48155 https://www.cve.org/CVERecord?id=CVE-2026-48155 Référence CVE CVE-2026-48156 https://www.cve.org/CVERecord?id=CVE-2026-48156 Référence CVE CVE-2026-4867 https://www.cve.org/CVERecord?id=CVE-2026-4867 Référence CVE CVE-2026-48710 https://www.cve.org/CVERecord?id=CVE-2026-48710 Référence CVE CVE-2026-48735 https://www.cve.org/CVERecord?id=CVE-2026-48735 Référence CVE CVE-2026-48817 https://www.cve.org/CVERecord?id=CVE-2026-48817 Référence CVE CVE-2026-48818 https://www.cve.org/CVERecord?id=CVE-2026-48818 Référence CVE CVE-2026-49460 https://www.cve.org/CVERecord?id=CVE-2026-49460 Référence CVE CVE-2026-49461 https://www.cve.org/CVERecord?id=CVE-2026-49461 Référence CVE CVE-2026-49476 https://www.cve.org/CVERecord?id=CVE-2026-49476 Référence CVE CVE-2026-49477 https://www.cve.org/CVERecord?id=CVE-2026-49477 Référence CVE CVE-2026-49844 https://www.cve.org/CVERecord?id=CVE-2026-49844 Référence CVE CVE-2026-49851 https://www.cve.org/CVERecord?id=CVE-2026-49851 Référence CVE CVE-2026-50010 https://www.cve.org/CVERecord?id=CVE-2026-50010 Référence CVE CVE-2026-50011 https://www.cve.org/CVERecord?id=CVE-2026-50011 Référence CVE CVE-2026-50020 https://www.cve.org/CVERecord?id=CVE-2026-50020 Référence CVE CVE-2026-50560 https://www.cve.org/CVERecord?id=CVE-2026-50560 Référence CVE CVE-2026-50645 https://www.cve.org/CVERecord?id=CVE-2026-50645 Référence CVE CVE-2026-50734 https://www.cve.org/CVERecord?id=CVE-2026-50734 Référence CVE CVE-2026-53537 https://www.cve.org/CVERecord?id=CVE-2026-53537 Référence CVE CVE-2026-53538 https://www.cve.org/CVERecord?id=CVE-2026-53538 Référence CVE CVE-2026-53539 https://www.cve.org/CVERecord?id=CVE-2026-53539 Référence CVE CVE-2026-53540 https://www.cve.org/CVERecord?id=CVE-2026-53540 Référence CVE CVE-2026-53917 https://www.cve.org/CVERecord?id=CVE-2026-53917 Référence CVE CVE-2026-54225 https://www.cve.org/CVERecord?id=CVE-2026-54225 Référence CVE CVE-2026-54282 https://www.cve.org/CVERecord?id=CVE-2026-54282 Référence CVE CVE-2026-54283 https://www.cve.org/CVERecord?id=CVE-2026-54283 Référence CVE CVE-2026-54286 https://www.cve.org/CVERecord?id=CVE-2026-54286 Référence CVE CVE-2026-54287 https://www.cve.org/CVERecord?id=CVE-2026-54287 Référence CVE CVE-2026-54288 https://www.cve.org/CVERecord?id=CVE-2026-54288 Référence CVE CVE-2026-54289 https://www.cve.org/CVERecord?id=CVE-2026-54289 Référence CVE CVE-2026-54290 https://www.cve.org/CVERecord?id=CVE-2026-54290 Référence CVE CVE-2026-54293 https://www.cve.org/CVERecord?id=CVE-2026-54293 Référence CVE CVE-2026-54428 https://www.cve.org/CVERecord?id=CVE-2026-54428 Référence CVE CVE-2026-54530 https://www.cve.org/CVERecord?id=CVE-2026-54530 Référence CVE CVE-2026-54531 https://www.cve.org/CVERecord?id=CVE-2026-54531 Référence CVE CVE-2026-54651 https://www.cve.org/CVERecord?id=CVE-2026-54651 Référence CVE CVE-2026-5516 https://www.cve.org/CVERecord?id=CVE-2026-5516 Référence CVE CVE-2026-57204 https://www.cve.org/CVERecord?id=CVE-2026-57204 Référence CVE CVE-2026-57819 https://www.cve.org/CVERecord?id=CVE-2026-57819 Référence CVE CVE-2026-59083 https://www.cve.org/CVERecord?id=CVE-2026-59083 Référence CVE CVE-2026-59084 https://www.cve.org/CVERecord?id=CVE-2026-59084 Référence CVE CVE-2026-59935 https://www.cve.org/CVERecord?id=CVE-2026-59935 Référence CVE CVE-2026-59936 https://www.cve.org/CVERecord?id=CVE-2026-59936 Référence CVE CVE-2026-59937 https://www.cve.org/CVERecord?id=CVE-2026-59937 Référence CVE CVE-2026-59938 https://www.cve.org/CVERecord?id=CVE-2026-59938 Référence CVE CVE-2026-60147 https://www.cve.org/CVERecord?id=CVE-2026-60147 Référence CVE CVE-2026-64958 https://www.cve.org/CVERecord?id=CVE-2026-64958 Référence CVE CVE-2026-65432 https://www.cve.org/CVERecord?id=CVE-2026-65432 Référence CVE CVE-2026-66053 https://www.cve.org/CVERecord?id=CVE-2026-66053 Référence CVE CVE-2026-66142 https://www.cve.org/CVERecord?id=CVE-2026-66142 Référence CVE CVE-2026-66143 https://www.cve.org/CVERecord?id=CVE-2026-66143 Référence CVE CVE-2026-66144 https://www.cve.org/CVERecord?id=CVE-2026-66144 Référence CVE CVE-2026-66713 https://www.cve.org/CVERecord?id=CVE-2026-66713 Référence CVE CVE-2026-6790 https://www.cve.org/CVERecord?id=CVE-2026-6790 Référence CVE CVE-2026-6918 https://www.cve.org/CVERecord?id=CVE-2026-6918 Référence CVE CVE-2026-69247 https://www.cve.org/CVERecord?id=CVE-2026-69247 Référence CVE CVE-2026-69248 https://www.cve.org/CVERecord?id=CVE-2026-69248 Référence CVE CVE-2026-69249 https://www.cve.org/CVERecord?id=CVE-2026-69249 Référence CVE CVE-2026-73088 https://www.cve.org/CVERecord?id=CVE-2026-73088 Référence CVE CVE-2026-73089 https://www.cve.org/CVERecord?id=CVE-2026-73089 Référence CVE CVE-2026-75878 Read more
No comment yet.
Scooped by Yannick Giquel
September 18, 9:53 AM

Trophées de la Cybersécurité 2026 : les candidatures sont ouvertes

Trophées de la Cybersécurité 2026 : les candidatures sont ouvertes | Cybersécurité | Scoop.it
La prochaine cérémonie de remise des Trophées de la Cybersécurité se tiendra le 19 novembre 2026 à Paris Expo Porte de Versailles. Le JDN est partenaire de l'événement.
No comment yet.
Scooped by Yannick Giquel
September 17, 1:07 PM

5G, fibre, cybersécurité… Les géants européens des télécoms mettent Bruxelles face à ses contradictions sur la souveraineté numérique

5G, fibre, cybersécurité… Les géants européens des télécoms mettent Bruxelles face à ses contradictions sur la souveraineté numérique | Cybersécurité | Scoop.it
No comment yet.
Scooped by Yannick Giquel
September 17, 9:23 AM

Multiples vulnérabilités dans les produits Cisco - CERT-FR

Multiples vulnérabilités dans les produits Cisco - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Exécution de code arbitraire à distance Injection SQL (SQLi) Non spécifié par l'éditeur Élévation de privilèges Systèmes affectés Adaptive Security Appliance (ASA), se référer au bulletin de sécurité de l'éditeur pour la liste des systèmes affectés (cf. section Documentation) Firewall Management Center (FMC), se référer au bulletin de sécurité de l'éditeur pour la liste des systèmes affectés (cf. section Documentation) Firewall Threat Defense (FTD), se référer au bulletin de sécurité de l'éditeur pour la liste des systèmes affectés (cf. section Documentation) ISE ou ISE-PIC versions 3.4 antérieures à 3.4 Patch 7 ISE versions 3.2 antérieures à 3.2 Patch 11 ISE versions 3.5 antérieures à 3.5 Patch 4 ISE versions antérieures à 3.1 Patch 12 ISE versions antérieures à 3.3 Patch 12 Cisco indique que les versions 3.2 et 3.1 de Identity Services Engine (ISE) ne seront plus supportées à partir du 30 novembre 2027 et n'ont pas reçu de correctif pour les vulnérabilités CVE-2026-20247, CVE-2026-20282, CVE-2026-20300, CVE-2026-76424, CVE-2026-76425, CVE-2026-76426, CVE-2026-76427 et CVE-2026-76428. La branche 3.0 ne l'est plus depuis le 13 juillet 2025. Concernant ISE-PIC, l'éditeur indique que ce produit n'est plus commercialisé et que la version 3.4 est la dernière encore maintenue. Résumé De multiples vulnérabilités ont été découvertes dans les produits Cisco. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire à distance, une élévation de privilèges et un déni de service à distance. Cisco indique que la vulnérabilité CVE-2026-76460 est activement exploitée. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Cisco cisco-sa-asa-ftd-logging-dos-ZXXNesfN du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-asa-ftd-logging-dos-ZXXNesfN Bulletin de sécurité Cisco cisco-sa-asaftd-dtls-dos-Kp57HkyO du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-asaftd-dtls-dos-Kp57HkyO Bulletin de sécurité Cisco cisco-sa-asaftd-eigrp-dos-GOhNejSj du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-asaftd-eigrp-dos-GOhNejSj Bulletin de sécurité Cisco cisco-sa-asaftd-ikev2cert-dos-uWyc2xtv du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-asaftd-ikev2cert-dos-uWyc2xtv Bulletin de sécurité Cisco cisco-sa-fmc-javarce-y2NypXwk du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-javarce-y2NypXwk Bulletin de sécurité Cisco cisco-sa-fmc-mulivulns-4PsnFwvx du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-mulivulns-4PsnFwvx Bulletin de sécurité Cisco cisco-sa-fmc-sftunn-codex-c3O4Jft2 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc-sftunn-codex-c3O4Jft2 Bulletin de sécurité Cisco cisco-sa-fmc2-multivulns-HXgcqRG du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmc2-multivulns-HXgcqRG Bulletin de sécurité Cisco cisco-sa-fmcftd-sftun-multivulns-WGVHOrN3 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-fmcftd-sftun-multivulns-WGVHOrN3 Bulletin de sécurité Cisco cisco-sa-ftd-tls1 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ftd-tls1.3-dos-dLxwFWgF Bulletin de sécurité Cisco cisco-sa-hardening-asaftdfmc-uvpPROhN du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-asaftdfmc-uvpPROhN Bulletin de sécurité Cisco cisco-sa-hardening-ise-XU5EwX5T du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-ise-XU5EwX5T Bulletin de sécurité Cisco cisco-sa-hardening-ndw1-psFvnrg du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-ndw1-psFvnrg Bulletin de sécurité Cisco cisco-sa-ISE-ABP-VNSW7Tn5 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ISE-ABP-VNSW7Tn5 Bulletin de sécurité Cisco cisco-sa-ise-cmd-inj-e2CuZCYZ du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-cmd-inj-e2CuZCYZ Bulletin de sécurité Cisco cisco-sa-ise-mult-vul-ymSsTLCc du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-mult-vul-ymSsTLCc Bulletin de sécurité Cisco cisco-sa-ise-multi-hrP9jQSQ du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-multi-hrP9jQSQ Bulletin de sécurité Cisco cisco-sa-ise-RADIUS-dos-wR3hYPMw du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-RADIUS-dos-wR3hYPMw Bulletin de sécurité Cisco cisco-sa-ise-rce-se7bYU57 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-rce-se7bYU57 Bulletin de sécurité Cisco cisco-sa-ise-sql-inj-3QTKR947 du 16 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-ise-sql-inj-3QTKR947 Support ISE Cisco https://www.cisco.com/c/en/us/support/security/identity-services-engine/series.html Référence CVE CVE-2026-20130 https://www.cve.org/CVERecord?id=CVE-2026-20130 Référence CVE CVE-2026-20135 https://www.cve.org/CVERecord?id=CVE-2026-20135 Référence CVE CVE-2026-20154 https://www.cve.org/CVERecord?id=CVE-2026-20154 Référence CVE CVE-2026-20176 https://www.cve.org/CVERecord?id=CVE-2026-20176 Référence CVE CVE-2026-20192 https://www.cve.org/CVERecord?id=CVE-2026-20192 Référence CVE CVE-2026-20194 https://www.cve.org/CVERecord?id=CVE-2026-20194 Référence CVE CVE-2026-20211 https://www.cve.org/CVERecord?id=CVE-2026-20211 Référence CVE CVE-2026-20222 https://www.cve.org/CVERecord?id=CVE-2026-20222 Référence CVE CVE-2026-20234 https://www.cve.org/CVERecord?id=CVE-2026-20234 Référence CVE CVE-2026-20237 https://www.cve.org/CVERecord?id=CVE-2026-20237 Référence CVE CVE-2026-20242 https://www.cve.org/CVERecord?id=CVE-2026-20242 Référence CVE CVE-2026-20247 https://www.cve.org/CVERecord?id=CVE-2026-20247 Référence CVE CVE-2026-20249 https://www.cve.org/CVERecord?id=CVE-2026-20249 Référence CVE CVE-2026-20250 https://www.cve.org/CVERecord?id=CVE-2026-20250 Référence CVE CVE-2026-20282 https://www.cve.org/CVERecord?id=CVE-2026-20282 Référence CVE CVE-2026-20283 https://www.cve.org/CVERecord?id=CVE-2026-20283 Référence CVE CVE-2026-20284 https://www.cve.org/CVERecord?id=CVE-2026-20284 Référence CVE CVE-2026-20287 https://www.cve.org/CVERecord?id=CVE-2026-20287 Référence CVE CVE-2026-20295 https://www.cve.org/CVERecord?id=CVE-2026-20295 Référence CVE CVE-2026-20300 https://www.cve.org/CVERecord?id=CVE-2026-20300 Référence CVE CVE-2026-20305 https://www.cve.org/CVERecord?id=CVE-2026-20305 Référence CVE CVE-2026-20306 https://www.cve.org/CVERecord?id=CVE-2026-20306 Référence CVE CVE-2026-20307 https://www.cve.org/CVERecord?id=CVE-2026-20307 Référence CVE CVE-2026-20322 https://www.cve.org/CVERecord?id=CVE-2026-20322 Référence CVE CVE-2026-20323 https://www.cve.org/CVERecord?id=CVE-2026-20323 Référence CVE CVE-2026-20324 https://www.cve.org/CVERecord?id=CVE-2026-20324 Référence CVE CVE-2026-20325 https://www.cve.org/CVERecord?id=CVE-2026-20325 Référence CVE CVE-2026-20326 https://www.cve.org/CVERecord?id=CVE-2026-20326 Référence CVE CVE-2026-20329 https://www.cve.org/CVERecord?id=CVE-2026-20329 Référence CVE CVE-2026-20330 https://www.cve.org/CVERecord?id=CVE-2026-20330 Référence CVE CVE-2026-20331 https://www.cve.org/CVERecord?id=CVE-2026-20331 Référence CVE CVE-2026-20332 https://www.cve.org/CVERecord?id=CVE-2026-20332 Référence CVE CVE-2026-20333 https://www.cve.org/CVERecord?id=CVE-2026-20333 Référence CVE CVE-2026-20334 https://www.cve.org/CVERecord?id=CVE-2026-20334 Référence CVE CVE-2026-20335 https://www.cve.org/CVERecord?id=CVE-2026-20335 Référence CVE CVE-2026-20336 https://www.cve.org/CVERecord?id=CVE-2026-20336 Référence CVE CVE-2026-20340 https://www.cve.org/CVERecord?id=CVE-2026-20340 Référence CVE CVE-2026-20341 https://www.cve.org/CVERecord?id=CVE-2026-20341 Référence CVE CVE-2026-20342 https://www.cve.org/CVERecord?id=CVE-2026-20342 Référence CVE CVE-2026-20343 https://www.cve.org/CVERecord?id=CVE-2026-20343 Référence CVE CVE-2026-20344 https://www.cve.org/CVERecord?id=CVE-2026-20344 Référence CVE CVE-2026-20352 https://www.cve.org/CVERecord?id=CVE-2026-20352 Référence CVE CVE-2026-20360 https://www.cve.org/CVERecord?id=CVE-2026-20360 Référence CVE CVE-2026-20361 https://www.cve.org/CVERecord?id=CVE-2026-20361 Référence CVE CVE-2026-76409 https://www.cve.org/CVERecord?id=CVE-2026-76409 Référence CVE CVE-2026-76412 https://www.cve.org/CVERecord?id=CVE-2026-76412 Référence CVE CVE-2026-76413 https://www.cve.org/CVERecord?id=CVE-2026-76413 Référence CVE CVE-2026-76420 https://www.cve.org/CVERecord?id=CVE-2026-76420 Référence CVE CVE-2026-76423 https://www.cve.org/CVERecord?id=CVE-2026-76423 Référence CVE CVE-2026-76424 https://www.cve.org/CVERecord?id=CVE-2026-76424 Référence CVE CVE-2026-76425 https://www.cve.org/CVERecord?id=CVE-2026-76425 Référence CVE CVE-2026-76426 https://www.cve.org/CVERecord?id=CVE-2026-76426 Référence CVE CVE-2026-76427 https://www.cve.org/CVERecord?id=CVE-2026-76427 Référence CVE CVE-2026-76428 https://www.cve.org/CVERecord?id=CVE-2026-76428 Référence CVE CVE-2026-76460 https://www.cve.org/CVERecord?id=CVE-2026-76460
No comment yet.
Scooped by Yannick Giquel
September 17, 5:23 AM

Le risque et la résilience de l'alliance entre IA et cybersécurité

Le risque et la résilience de l'alliance entre IA et cybersécurité | Cybersécurité | Scoop.it
L'intelligence artificielle est devenue à la fois la cible et l'outil de la cybersécurité.Les cybercriminels utilisent désormais des systèmes intelligents pour multiplier et dissimuler leurs attaques...
No comment yet.
Scooped by Yannick Giquel
September 16, 8:09 AM

Multiples vulnérabilités dans Docker - CERT-FR

Multiples vulnérabilités dans Docker - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Exécution de code arbitraire à distance Systèmes affectés Docker Sandboxes versions antérieures à 0.42.0 Résumé De multiples vulnérabilités ont été découvertes dans Docker. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire à distance, une atteinte à la confidentialité des données et une atteinte à l'intégrité des données. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Docker #docker-sandboxes-0420-security-update-cve-2026-77179-and-cve-2026-79994 du 07 septembre 2026 https://docs.docker.com/security/security-announcements/#docker-sandboxes-0420-security-update-cve-2026-77179-and-cve-2026-79994 Référence CVE CVE-2026-77179 https://www.cve.org/CVERecord?id=CVE-2026-77179 Référence CVE CVE-2026-79994 https://www.cve.org/CVERecord?id=CVE-2026-79994
No comment yet.
Scooped by Yannick Giquel
September 16, 1:54 AM

Oracle dévoile Java 27, tourné vers l’IA et la cryptographie post ...

Oracle dévoile Java 27, tourné vers l’IA et la cryptographie post ... | Cybersécurité | Scoop.it
Java 27 illustre une préoccupation grandissante dans l’industrie du logiciel : protéger dès maintenant les données sensibles contre la menace dite du « harvest now, decrypt later », qui consiste à intercepter des communications chiffrées aujourd’hui pour les déchiffrer plus tard grâce à de futurs...
No comment yet.
Scooped by Yannick Giquel
September 15, 8:22 AM

Multiples vulnérabilités dans les produits Cisco - CERT-FR

Multiples vulnérabilités dans les produits Cisco - CERT-FR | Cybersécurité | Scoop.it
Risques Contournement de la politique de sécurité Déni de service à distance Exécution de code arbitraire à distance Injection de code indirecte à distance (XSS) Injection SQL (SQLi) Systèmes affectés AsyncOS pour Secure Email Gateway versions 16.0.x antérieures à 16.0.4-3021 AsyncOS pour Secure Email Gateway versions 16.5.x antérieures à 16.5.0-780 AsyncOS pour Secure Email Gateway versions antérieures à 15.5.5-0141 Secure Email and Web Manager versions 16.x antérieures à 16.5.0-429 Secure Email and Web Manager versions antérieures à 15.5.5-006 Secure Email Gateway versions 16.x antérieures à 16.5.0-780 Secure Email Gateway versions antérieures à 15.5.5-014 Résumé De multiples vulnérabilités ont été découvertes dans les produits Cisco. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire à distance, un déni de service à distance et une injection SQL (SQLi). Cisco indique que la vulnérabilité CVE-2026-76461 est activement exploitée. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Cisco cisco-sa-esa-inj-2bLVGmhX du 14 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-esa-inj-2bLVGmhX Bulletin de sécurité Cisco cisco-sa-hardening-esa-dfCrfXkm du 14 septembre 2026 https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-hardening-esa-dfCrfXkm Référence CVE CVE-2026-20353 https://www.cve.org/CVERecord?id=CVE-2026-20353 Référence CVE CVE-2026-76440 https://www.cve.org/CVERecord?id=CVE-2026-76440 Référence CVE CVE-2026-76441 https://www.cve.org/CVERecord?id=CVE-2026-76441 Référence CVE CVE-2026-76442 https://www.cve.org/CVERecord?id=CVE-2026-76442 Référence CVE CVE-2026-76443 https://www.cve.org/CVERecord?id=CVE-2026-76443 Référence CVE CVE-2026-76461 https://www.cve.org/CVERecord?id=CVE-2026-76461
No comment yet.
Scooped by Yannick Giquel
September 14, 11:08 AM

Multiples vulnérabilités dans MongoDB - CERT-FR

Multiples vulnérabilités dans MongoDB - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Systèmes affectés C Driver versions antérieures à 1.30.10 C Driver versions antérieures à 2.5.3 C# Driver versions antérieures à 3.11.2 C++ Driver versions antérieures à 4.5.3 Core Server versions antérieures à 7.0.43 Core Server versions antérieures à 8.0.32 Core Server versions antérieures à 8.3.11 Core Server versions antérieures à 9.1.0-rc0 Go Driver versions antérieures à 1.17.10 Go Driver versions antérieures à 2.9.1 Java Driver versions antérieures à 5.11.1 PHP Driver versions antérieures à 1.21.5 PHP Driver versions antérieures à 2.4.2 PHP Laravel MongoDB Integration versions antérieures à 5.11.0 Python Driver versions antérieures à 4.18.1 Ruby Driver versions antérieures à 2.26.0 Rust Driver versions antérieures à 3.9.1 Résumé De multiples vulnérabilités ont été découvertes dans MongoDB. Certaines d'entre elles permettent à un attaquant de provoquer un déni de service à distance, une atteinte à la confidentialité des données et une atteinte à l'intégrité des données. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité MongoDB CDRIVER-6416 du 10 septembre 2026 https://jira.mongodb.org/browse/CDRIVER-6416 Bulletin de sécurité MongoDB CDRIVER-6427 du 10 septembre 2026 https://jira.mongodb.org/browse/CDRIVER-6427 Bulletin de sécurité MongoDB CSHARP-6177 du 10 septembre 2026 https://jira.mongodb.org/browse/CSHARP-6177 Bulletin de sécurité MongoDB CSHARP-6190 du 10 septembre 2026 https://jira.mongodb.org/browse/CSHARP-6190 Bulletin de sécurité MongoDB CXX-3556 du 10 septembre 2026 https://jira.mongodb.org/browse/CXX-3556 Bulletin de sécurité MongoDB GODRIVER-4081 du 10 septembre 2026 https://jira.mongodb.org/browse/GODRIVER-4081 Bulletin de sécurité MongoDB JAVA-6276 du 10 septembre 2026 https://jira.mongodb.org/browse/JAVA-6276 Bulletin de sécurité MongoDB JAVA-6283 du 10 septembre 2026 https://jira.mongodb.org/browse/JAVA-6283 Bulletin de sécurité MongoDB PHPLARA-260 du 10 septembre 2026 https://jira.mongodb.org/browse/PHPLARA-260 Bulletin de sécurité MongoDB PHPLARA-265 du 10 septembre 2026 https://jira.mongodb.org/browse/PHPLARA-265 Bulletin de sécurité MongoDB PHPLIB-1929 du 10 septembre 2026 https://jira.mongodb.org/browse/PHPLIB-1929 Bulletin de sécurité MongoDB PYTHON-5994 du 10 septembre 2026 https://jira.mongodb.org/browse/PYTHON-5994 Bulletin de sécurité MongoDB RUBY-3941 du 10 septembre 2026 https://jira.mongodb.org/browse/RUBY-3941 Bulletin de sécurité MongoDB RUST-2469 du 10 septembre 2026 https://jira.mongodb.org/browse/RUST-2469 Bulletin de sécurité MongoDB SERVER-134063 du 11 septembre 2026 https://jira.mongodb.org/browse/SERVER-134063 Référence CVE CVE-2026-88022 https://www.cve.org/CVERecord?id=CVE-2026-88022 Référence CVE CVE-2026-88023 https://www.cve.org/CVERecord?id=CVE-2026-88023 Référence CVE CVE-2026-88024 https://www.cve.org/CVERecord?id=CVE-2026-88024 Référence CVE CVE-2026-88025 https://www.cve.org/CVERecord?id=CVE-2026-88025 Référence CVE CVE-2026-88026 https://www.cve.org/CVERecord?id=CVE-2026-88026 Référence CVE CVE-2026-88027 https://www.cve.org/CVERecord?id=CVE-2026-88027 Référence CVE CVE-2026-88028 https://www.cve.org/CVERecord?id=CVE-2026-88028 Référence CVE CVE-2026-88029 https://www.cve.org/CVERecord?id=CVE-2026-88029 Référence CVE CVE-2026-88030 https://www.cve.org/CVERecord?id=CVE-2026-88030 Référence CVE CVE-2026-88031 https://www.cve.org/CVERecord?id=CVE-2026-88031 Référence CVE CVE-2026-88032 https://www.cve.org/CVERecord?id=CVE-2026-88032 Référence CVE CVE-2026-88033 https://www.cve.org/CVERecord?id=CVE-2026-88033 Référence CVE CVE-2026-88034 https://www.cve.org/CVERecord?id=CVE-2026-88034 Référence CVE CVE-2026-88035 https://www.cve.org/CVERecord?id=CVE-2026-88035 Référence CVE CVE-2026-88036 https://www.cve.org/CVERecord?id=CVE-2026-88036 Référence CVE CVE-2026-89099 https://www.cve.org/CVERecord?id=CVE-2026-89099
No comment yet.
Scooped by Yannick Giquel
September 14, 11:08 AM

Multiples vulnérabilités dans MISP - CERT-FR

Multiples vulnérabilités dans MISP - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Falsification de requêtes côté serveur (SSRF) Injection de code indirecte à distance (XSS) Injection de requêtes illégitimes par rebond (CSRF) Systèmes affectés MISP versions antérieures à 2.5.45 Résumé De multiples vulnérabilités ont été découvertes dans MISP. Certaines d'entre elles permettent à un attaquant de provoquer un déni de service à distance, une atteinte à la confidentialité des données et une atteinte à l'intégrité des données. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité MISP CVE-2026-85216 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85216 Bulletin de sécurité MISP CVE-2026-85221 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85221 Bulletin de sécurité MISP CVE-2026-85226 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85226 Bulletin de sécurité MISP CVE-2026-85227 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85227 Bulletin de sécurité MISP CVE-2026-85230 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85230 Bulletin de sécurité MISP CVE-2026-85236 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85236 Bulletin de sécurité MISP CVE-2026-85237 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85237 Bulletin de sécurité MISP CVE-2026-85238 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85238 Bulletin de sécurité MISP CVE-2026-85239 du 03 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-85239 Bulletin de sécurité MISP CVE-2026-86342 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86342 Bulletin de sécurité MISP CVE-2026-86347 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86347 Bulletin de sécurité MISP CVE-2026-86351 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86351 Bulletin de sécurité MISP CVE-2026-86408 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86408 Bulletin de sécurité MISP CVE-2026-86417 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86417 Bulletin de sécurité MISP CVE-2026-86418 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86418 Bulletin de sécurité MISP CVE-2026-86419 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86419 Bulletin de sécurité MISP CVE-2026-86440 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86440 Bulletin de sécurité MISP CVE-2026-86441 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86441 Bulletin de sécurité MISP CVE-2026-86452 du 07 septembre 2026 https://vulnerability.circl.lu/vuln/CVE-2026-86452 Référence CVE CVE-2026-85216 https://www.cve.org/CVERecord?id=CVE-2026-85216 Référence CVE CVE-2026-85221 https://www.cve.org/CVERecord?id=CVE-2026-85221 Référence CVE CVE-2026-85226 https://www.cve.org/CVERecord?id=CVE-2026-85226 Référence CVE CVE-2026-85227 https://www.cve.org/CVERecord?id=CVE-2026-85227 Référence CVE CVE-2026-85230 https://www.cve.org/CVERecord?id=CVE-2026-85230 Référence CVE CVE-2026-85236 https://www.cve.org/CVERecord?id=CVE-2026-85236 Référence CVE CVE-2026-85237 https://www.cve.org/CVERecord?id=CVE-2026-85237 Référence CVE CVE-2026-85238 https://www.cve.org/CVERecord?id=CVE-2026-85238 Référence CVE CVE-2026-85239 https://www.cve.org/CVERecord?id=CVE-2026-85239 Référence CVE CVE-2026-86342 https://www.cve.org/CVERecord?id=CVE-2026-86342 Référence CVE CVE-2026-86347 https://www.cve.org/CVERecord?id=CVE-2026-86347 Référence CVE CVE-2026-86351 https://www.cve.org/CVERecord?id=CVE-2026-86351 Référence CVE CVE-2026-86408 https://www.cve.org/CVERecord?id=CVE-2026-86408 Référence CVE CVE-2026-86417 https://www.cve.org/CVERecord?id=CVE-2026-86417 Référence CVE CVE-2026-86418 https://www.cve.org/CVERecord?id=CVE-2026-86418 Référence CVE CVE-2026-86419 https://www.cve.org/CVERecord?id=CVE-2026-86419 Référence CVE CVE-2026-86440 https://www.cve.org/CVERecord?id=CVE-2026-86440 Référence CVE CVE-2026-86441 https://www.cve.org/CVERecord?id=CVE-2026-86441 Référence CVE CVE-2026-86452 https://www.cve.org/CVERecord?id=CVE-2026-86452
No comment yet.
Scooped by Yannick Giquel
September 11, 2:23 PM

Quand le phishing généré par IA atteint un taux de clic de 54 %, sécuriser les identités n'est plus option !

Quand le phishing généré par IA atteint un taux de clic de 54 %, sécuriser les identités n'est plus option ! | Cybersécurité | Scoop.it
Le phishing (hameçonnage) a fonctionné pendant des années pour une raison simple : il exploite le maillon le plus faible : l'utilisateur.
No comment yet.
Scooped by Yannick Giquel
September 11, 10:38 AM

Multiples vulnérabilités dans le noyau Linux de Red Hat - CERT-FR

Multiples vulnérabilités dans le noyau Linux de Red Hat - CERT-FR | Cybersécurité | Scoop.it
Risques Atteinte à l'intégrité des données Atteinte à la confidentialité des données Contournement de la politique de sécurité Déni de service à distance Exécution de code arbitraire Non spécifié par l'éditeur Élévation de privilèges Systèmes affectés Red Hat CodeReady Linux Builder for ARM 64 - Extended Update Support 10.0 aarch64 Red Hat CodeReady Linux Builder for ARM 64 8 aarch64 Red Hat CodeReady Linux Builder for IBM z Systems - Extended Update Support 10.0 s390x Red Hat CodeReady Linux Builder for Power, little endian - Extended Update Support 10.0 ppc64le Red Hat CodeReady Linux Builder for Power, little endian 8 ppc64le Red Hat CodeReady Linux Builder for x86_64 - Extended Update Support 10.0 x86_64 Red Hat CodeReady Linux Builder for x86_64 8 x86_64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 10.0 aarch64 Red Hat Enterprise Linux for ARM 64 - 4 years of updates 9.4 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 8.10 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Life Cycle 9.4 aarch64 Red Hat Enterprise Linux for ARM 64 - Extended Update Support 10.0 aarch64 Red Hat Enterprise Linux for ARM 64 8 aarch64 Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 10.0 s390x Red Hat Enterprise Linux for IBM z Systems - 4 years of updates 9.4 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 8.10 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Life Cycle 9.4 s390x Red Hat Enterprise Linux for IBM z Systems - Extended Update Support 10.0 s390x Red Hat Enterprise Linux for IBM z Systems 8 s390x Red Hat Enterprise Linux for Power, little endian - 4 years of support 10.0 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 8.10 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Life Cycle 9.4 ppc64le Red Hat Enterprise Linux for Power, little endian - Extended Update Support 10.0 ppc64le Red Hat Enterprise Linux for Power, little endian 8 ppc64le Red Hat Enterprise Linux for Real Time 8 x86_64 Red Hat Enterprise Linux for Real Time for NFV 8 x86_64 Red Hat Enterprise Linux for x86_64 - 4 years of updates 10.0 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 8.10 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle 9.4 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle Long Life 8.4 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Life Cycle Long Life 8.6 x86_64 Red Hat Enterprise Linux for x86_64 - Extended Update Support 10.0 x86_64 Red Hat Enterprise Linux for x86_64 - Update Services for SAP Solutions 9.4 x86_64 Red Hat Enterprise Linux for x86_64 8 x86_64 Red Hat Enterprise Linux Server - AUS 8.4 x86_64 Red Hat Enterprise Linux Server - AUS 8.6 x86_64 Red Hat Enterprise Linux Server - AUS 9.4 x86_64 Red Hat Enterprise Linux Server - Extended Life Cycle Support (for IBM z Systems) 7 s390x Red Hat Enterprise Linux Server - Extended Life Cycle Support 7 x86_64 Red Hat Enterprise Linux Server - Extended Life Cycle Support for IBM Power, big endian 7 ppc64 Red Hat Enterprise Linux Server - Extended Life Cycle Support for IBM Power, little endian 7 ppc64le Red Hat Enterprise Linux Server for Power LE - Update Services for SAP Solutions 9.4 ppc64le Résumé De multiples vulnérabilités ont été découvertes dans le noyau Linux de Red Hat. Certaines d'entre elles permettent à un attaquant de provoquer une exécution de code arbitraire, une élévation de privilèges et un déni de service à distance. Solutions Se référer au bulletin de sécurité de l'éditeur pour l'obtention des correctifs (cf. section Documentation). Documentation Bulletin de sécurité Red Hat RHSA-2026:63538 du 04 septembre 2026 https://access.redhat.com/errata/RHSA-2026:63538 Bulletin de sécurité Red Hat RHSA-2026:64767 du 08 septembre 2026 https://access.redhat.com/errata/RHSA-2026:64767 Bulletin de sécurité Red Hat RHSA-2026:64770 du 08 septembre 2026 https://access.redhat.com/errata/RHSA-2026:64770 Bulletin de sécurité Red Hat RHSA-2026:65710 du 09 septembre 2026 https://access.redhat.com/errata/RHSA-2026:65710 Bulletin de sécurité Red Hat RHSA-2026:65711 du 09 septembre 2026 https://access.redhat.com/errata/RHSA-2026:65711 Bulletin de sécurité Red Hat RHSA-2026:65712 du 09 septembre 2026 https://access.redhat.com/errata/RHSA-2026:65712 Bulletin de sécurité Red Hat RHSA-2026:66000 du 09 septembre 2026 https://access.redhat.com/errata/RHSA-2026:66000 Bulletin de sécurité Red Hat RHSA-2026:66324 du 10 septembre 2026 https://access.redhat.com/errata/RHSA-2026:66324 Bulletin de sécurité Red Hat RHSA-2026:66325 du 10 septembre 2026 https://access.redhat.com/errata/RHSA-2026:66325 Référence CVE CVE-2021-47600 https://www.cve.org/CVERecord?id=CVE-2021-47600 Référence CVE CVE-2023-52924 https://www.cve.org/CVERecord?id=CVE-2023-52924 Référence CVE CVE-2025-38403 https://www.cve.org/CVERecord?id=CVE-2025-38403 Référence CVE CVE-2025-40149 https://www.cve.org/CVERecord?id=CVE-2025-40149 Référence CVE CVE-2025-68745 https://www.cve.org/CVERecord?id=CVE-2025-68745 Référence CVE CVE-2026-17523 https://www.cve.org/CVERecord?id=CVE-2026-17523 Référence CVE CVE-2026-31411 https://www.cve.org/CVERecord?id=CVE-2026-31411 Référence CVE CVE-2026-43114 https://www.cve.org/CVERecord?id=CVE-2026-43114 Référence CVE CVE-2026-43493 https://www.cve.org/CVERecord?id=CVE-2026-43493 Référence CVE CVE-2026-45998 https://www.cve.org/CVERecord?id=CVE-2026-45998 Référence CVE CVE-2026-46056 https://www.cve.org/CVERecord?id=CVE-2026-46056 Référence CVE CVE-2026-46099 https://www.cve.org/CVERecord?id=CVE-2026-46099 Référence CVE CVE-2026-46117 https://www.cve.org/CVERecord?id=CVE-2026-46117 Référence CVE CVE-2026-46120 https://www.cve.org/CVERecord?id=CVE-2026-46120 Référence CVE CVE-2026-46145 https://www.cve.org/CVERecord?id=CVE-2026-46145 Référence CVE CVE-2026-46149 https://www.cve.org/CVERecord?id=CVE-2026-46149 Référence CVE CVE-2026-46155 https://www.cve.org/CVERecord?id=CVE-2026-46155 Référence CVE CVE-2026-52917 https://www.cve.org/CVERecord?id=CVE-2026-52917 Référence CVE CVE-2026-52942 https://www.cve.org/CVERecord?id=CVE-2026-52942 Référence CVE CVE-2026-52986 https://www.cve.org/CVERecord?id=CVE-2026-52986 Référence CVE CVE-2026-53002 https://www.cve.org/CVERecord?id=CVE-2026-53002 Référence CVE CVE-2026-53006 https://www.cve.org/CVERecord?id=CVE-2026-53006 Référence CVE CVE-2026-53009 https://www.cve.org/CVERecord?id=CVE-2026-53009 Référence CVE CVE-2026-53016 https://www.cve.org/CVERecord?id=CVE-2026-53016 Référence CVE CVE-2026-53071 https://www.cve.org/CVERecord?id=CVE-2026-53071 Référence CVE CVE-2026-53091 https://www.cve.org/CVERecord?id=CVE-2026-53091 Référence CVE CVE-2026-53196 https://www.cve.org/CVERecord?id=CVE-2026-53196 Référence CVE CVE-2026-53246 https://www.cve.org/CVERecord?id=CVE-2026-53246 Référence CVE CVE-2026-63801 https://www.cve.org/CVERecord?id=CVE-2026-63801 Référence CVE CVE-2026-63886 https://www.cve.org/CVERecord?id=CVE-2026-63886 Référence CVE CVE-2026-63971 https://www.cve.org/CVERecord?id=CVE-2026-63971 Référence CVE CVE-2026-64007 https://www.cve.org/CVERecord?id=CVE-2026-64007 Référence CVE CVE-2026-64015 https://www.cve.org/CVERecord?id=CVE-2026-64015 Référence CVE CVE-2026-64113 https://www.cve.org/CVERecord?id=CVE-2026-64113 Référence CVE CVE-2026-64191 https://www.cve.org/CVERecord?id=CVE-2026-64191 Référence CVE CVE-2026-64268 https://www.cve.org/CVERecord?id=CVE-2026-64268 Référence CVE CVE-2026-64304 https://www.cve.org/CVERecord?id=CVE-2026-64304 Référence CVE CVE-2026-64563 https://www.cve.org/CVERecord?id=CVE-2026-64563 Référence CVE CVE-2026-68117 https://www.cve.org/CVERecord?id=CVE-2026-68117 Référence CVE CVE-2026-68300 https://www.cve.org/CVERecord?id=CVE-2026-68300 Référence CVE CVE-2026-68315 https://www.cve.org/CVERecord?id=CVE-2026-68315 Référence CVE CVE-2026-68343 https://www.cve.org/CVERecord?id=CVE-2026-68343 Référence CVE CVE-2026-68376 https://www.cve.org/CVERecord?id=CVE-2026-68376 Référence CVE CVE-2026-72129 https://www.cve.org/CVERecord?id=CVE-2026-72129 Référence CVE CVE-2026-74480 https://www.cve.org/CVERecord?id=CVE-2026-74480
No comment yet.